Plain-English security writing
No fear-mongering, no acronym soup. The questions Australian teams ask before they buy a test, written down so you can brief a vendor, including us.
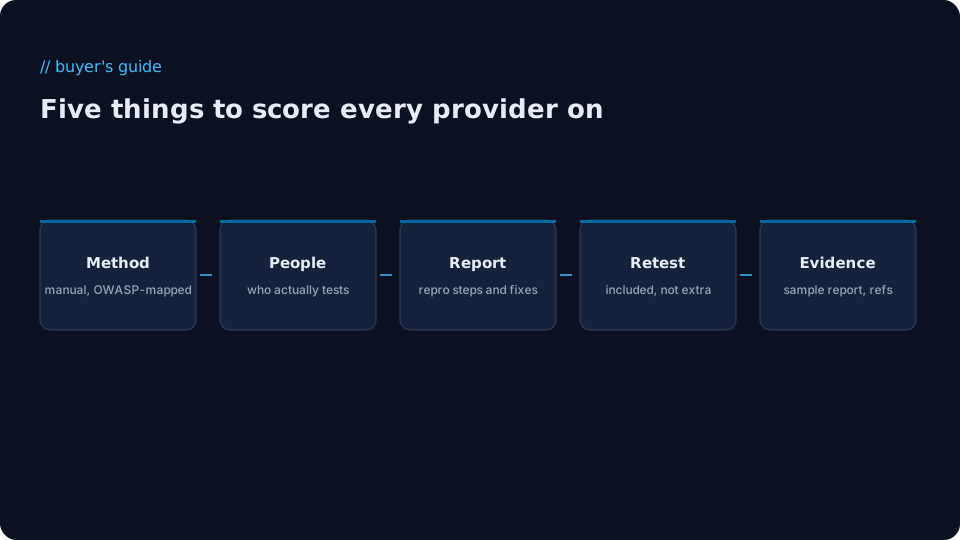
How to choose a penetration testing company in Australia
A buyer's guide to choosing a penetration testing company in Australia: five things that separate good providers from scanner runs, and 15 questions to ask.
Read post >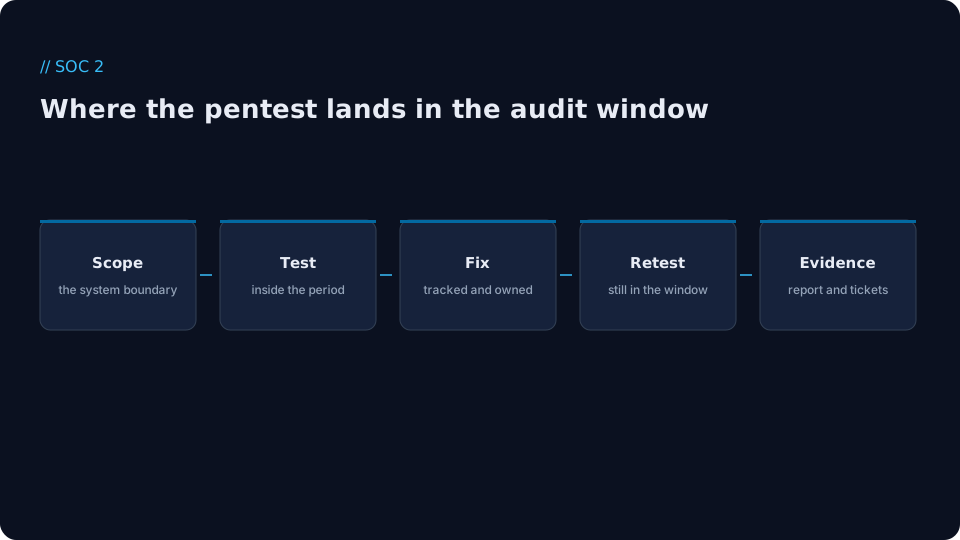
SOC 2 penetration testing: is it required, and when should you do it?
Does SOC 2 require a penetration test? Which Trust Services Criteria it supports, how to time it for Type I vs Type II, and what evidence to give your auditor.
Read post >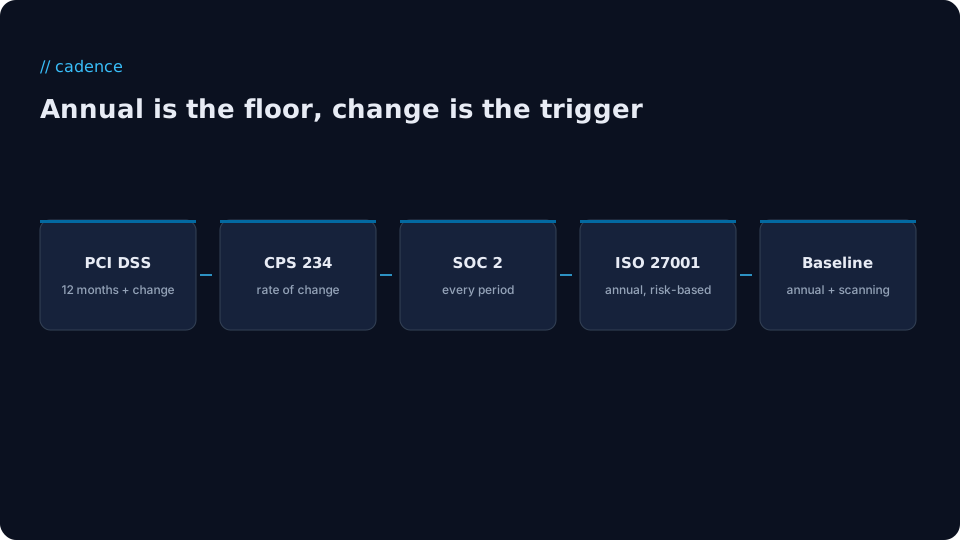
How often should you do penetration testing?
How often to penetration test: the annual baseline, what counts as a significant change, and the cadences PCI DSS, SOC 2, ISO 27001 and APRA CPS 234 expect.
Read post >
How to scope a web application penetration test
What to put in the rules of engagement, which roles to include, and how to avoid buying a test that misses the actual risk.
Read post >
APRA CPS 234 and security testing: what actually satisfies the standard
How APRA-regulated entities should brief a pentest so the report maps to information-security control testing, not a generic scan.
Read post >
Essential Eight and penetration testing: how they fit together
The ACSC maturity model is a control program. A pentest is how you find out whether those controls survive a motivated attacker.
Read post >
ISO 27001 penetration testing in Australia
Where independent testing sits in Annex A, what auditors actually look for in a report, and how often to retest.
Read post >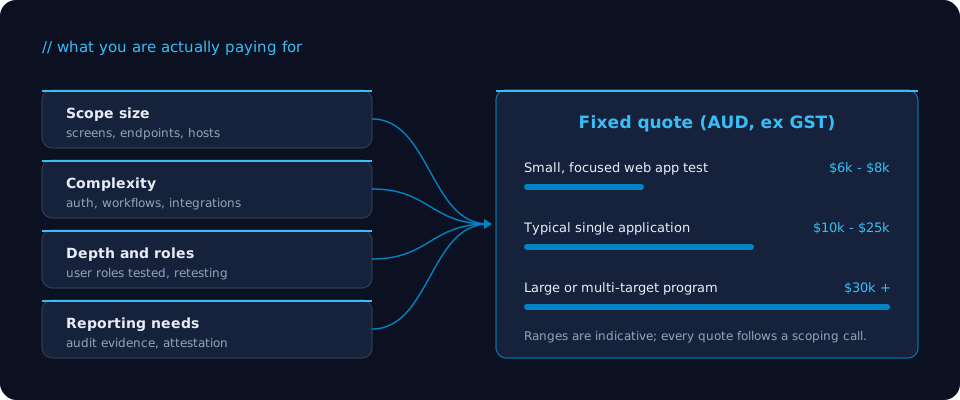
How much does a penetration test cost in Australia?
Typical price ranges for Australian pentests, what drives the cost up or down, and how to compare quotes properly.
Read post >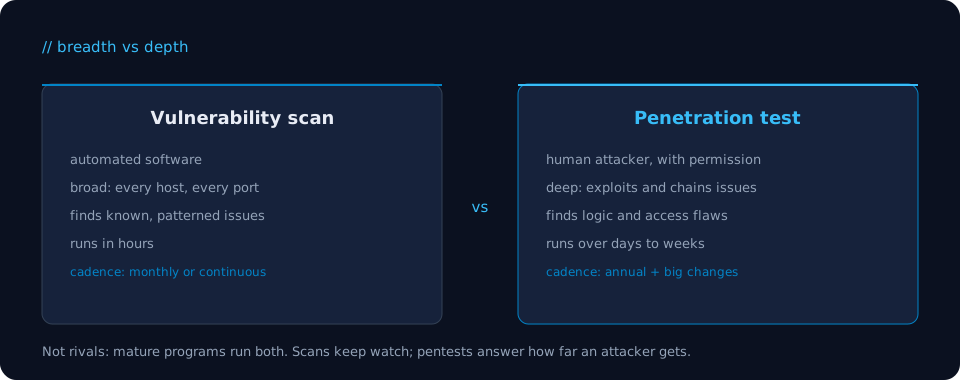
Penetration testing vs vulnerability scanning: what's the difference?
Both find security problems, but they answer different questions. When a scan is enough, and when you need a human attacker.
Read post >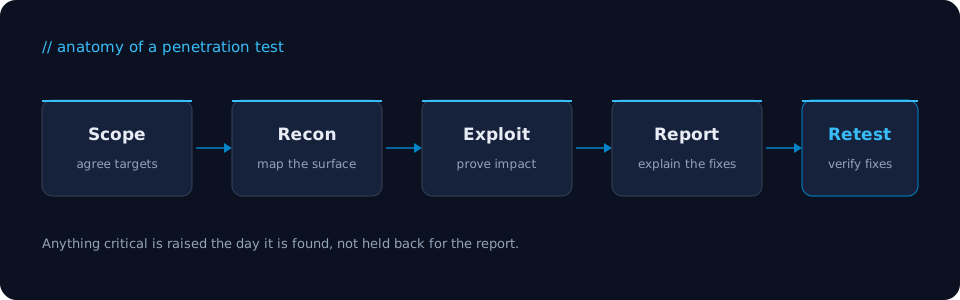
What is penetration testing? A plain-English guide
What actually happens during a pentest, what you get at the end, and how to tell a real one from a rebadged scan.
Read post >